今天在網路上看到很有興趣的Linux Distribution搜尋排名比較,請參考原文網址,其中DistroWatch根據使用者點閱Linux Distribution網頁所得出的結果如下:
1. Ubuntu
2. Fedora
3. Mint
4. OpenSUSE
5. Debian
6. PCLinuxOS
7. Mandriva
8. Sabayon
9. Arch
10. Puppy
然而,此統計數據以Linux Desktop OS Distribution為基礎,所以Android沒在排名之中。
於是,作者利用Google Trend所得出的結果,則是Android排名第一。
2010年11月2日 星期二

2010年10月11日 星期一
[打造簡易作業系統 - 以GNU Assembler組合語言撰寫] (五) 使用Local Descriptor Table (LDT)
上篇文章使用Global Descriptor Table (GDT)儲存Code Segment (CS)與Data Segment (DS)的資訊,以便能在保護模式下成功地執行程式碼與存取資料。本篇說明如何設定LDT,以便能執行位於LDT的程式碼。
LDT之介紹
LDT實現作業系統多個程序功能 (multiple processes),其特色為各個程序有自己的位址空間彼此互不干擾,每個程序會有各自的LDT,當作業系統欲執行某一程序時,作業系統會找出其對應的LDT,以便能執行該程序。詳細資料請參考Local Descriptor Table。
LDT相關設定
LDT設定分成兩大步驟如下所述:
1. 在GDT表裡設定一個LDT entry (Configure a LDT Entry in GDT)
參考Figure 1,其每個欄位所應設定值如Table 1所示:

2. 設定LDT表
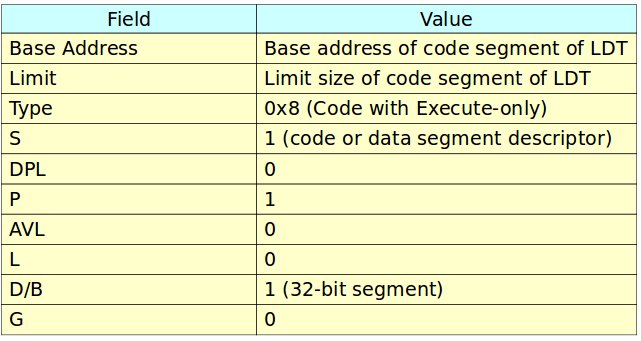
LDT表設定code segment/data segment相關資訊,其設定值如Table 2所示。
請參考上篇文章的"Boot Loader 程式碼"。
作業系統程式碼
Figure 2為作業系統程式碼,此作業系統程式碼運行於32位元保護模式,一開始定義三個Segment Descriptor (NULL、CODE32、VIDEO與LDT),其中VIDEO的基底位址為0xB8000,詳情請參考Printing to Screen。接著定義GDT的長度、定義Code32、Data、VIDEO與LDT的segment selector、定義輸出的字串、定義GDTPtr與定義LDT表。
16位元real mode程式碼 (os_main)中,執行若干任務如下所述:
pm.h標頭檔
編譯程式碼
請參照此篇的Makefile程式碼
其編譯訊息如下所示:
QEMU測試結果

【Reference】
[1] Solrex - 使用開源軟體-自己動手寫作業系統
[2] Intel 64 and IA-32 Architectures. Software Developer's Manual. Volume 3A
[3] 30天打造OS!作業系統自作入門
[4] Jserv's Blog
[5] X86 開機流程小記
[6] Linux assemblers: A comparison of GAS and NASM
[7] linux-source-2.6.31
LDT之介紹
LDT實現作業系統多個程序功能 (multiple processes),其特色為各個程序有自己的位址空間彼此互不干擾,每個程序會有各自的LDT,當作業系統欲執行某一程序時,作業系統會找出其對應的LDT,以便能執行該程序。詳細資料請參考Local Descriptor Table。
LDT相關設定
LDT設定分成兩大步驟如下所述:
1. 在GDT表裡設定一個LDT entry (Configure a LDT Entry in GDT)
參考Figure 1,其每個欄位所應設定值如Table 1所示:
Figure 1. Segment Descriptor

Table 1. LDT entry configuration in GDT
Table 1. LDT entry configuration in GDT
2. 設定LDT表
LDT表設定code segment/data segment相關資訊,其設定值如Table 2所示。
Table 2. LDT entry configuration in LDT
Boot Loader程式碼請參考上篇文章的"Boot Loader 程式碼"。
作業系統程式碼
Figure 2為作業系統程式碼,此作業系統程式碼運行於32位元保護模式,一開始定義三個Segment Descriptor (NULL、CODE32、VIDEO與LDT),其中VIDEO的基底位址為0xB8000,詳情請參考Printing to Screen。接著定義GDT的長度、定義Code32、Data、VIDEO與LDT的segment selector、定義輸出的字串、定義GDTPtr與定義LDT表。
/* os.S
*
*/

#include "pm.h"

.code16
.text
  jmp os_main

# Segment descritors for GDT
LABEL_GDT_NULL: SEG_DESC 0, 0, 0
LABEL_GDT_CODE: SEG_DESC 0, (PECode32Len - 1), (DESC_ATTR_TYPE_CD_ER | DESC_ATTR_D)
LABEL_GDT_DATA: SEG_DESC 0, (DataLen - 1), (DESC_ATTR_TYPE_CD_RW)
LABEL_GDT_VIDEO: SEG_DESC 0xB8000, 0xFFFF, (DESC_ATTR_TYPE_CD_RW)
LABEL_GDT_LDT: SEG_DESC     0, (LDTLen -1), (DESC_ATTR_TYPE_LDT)

# The length of GDT
.set GdtLen, (. - LABEL_GDT_NULL)

# Segment selectors
.set SegSelectorCode32, (LABEL_GDT_CODE - LABEL_GDT_NULL)
.set SegSelectorData,     (LABEL_GDT_DATA - LABEL_GDT_NULL)
.set SegSelectorVideo,     (LABEL_GDT_VIDEO - LABEL_GDT_NULL)
.set SegSelectorLDT,     (LABEL_GDT_LDT - LABEL_GDT_NULL)

# data segment
LABEL_DATA:
Msg1:     .ascii "Welcome to Protect mode in GDT.\0"
Msg2:     .ascii "Welcome to Protect mode in LDT.\0"
Msg3:     .ascii "This is signed by Adrian.\0"

.set     Msg1Offset, (Msg1 - LABEL_DATA)
.set     Msg2Offset, (Msg2 - LABEL_DATA)
.set     Msg3Offset, (Msg3 - LABEL_DATA)

.set DataLen, (. - LABEL_DATA)

# GDTR pointer
LABEL_GDTR:
  .2byte (GdtLen - 1)     # Limit field
  .4byte 0                 # base field

# LDT information
LABEL_LDT:
LABEL_LDT_ENTRY: SEG_DESC 0, (LDT_CODE32_LEN - 1), (DESC_ATTR_TYPE_CD_E | DESC_ATTR_D)

# length of LDT
.set LDTLen, (. - LABEL_LDT)

# LDT selector
.set SegSelectorLDTCode32,     (LABEL_LDT_ENTRY - LABEL_LDT + SA_TIL)


# real-mode OS code
os_main:
  mov %cs, %ax
  mov %ax, %ds
  mov %ax, %ss
  mov %ax, %es


  /* Set gdt for code segment */
  InitSegDescriptor LABEL_PE_CODE32, LABEL_GDT_CODE
  InitSegDescriptor LABEL_DATA, LABEL_GDT_DATA
  InitSegDescriptor LABEL_LDT, LABEL_GDT_LDT
  InitSegDescriptor LABEL_PE_LDT_CODE32, LABEL_LDT_ENTRY

  /* Set GDTR */
  xor     %ax, %ax
  mov     %cs, %ax
  shl     $4, %eax
  addl    $LABEL_GDT_NULL, %eax
  movl     %eax, (LABEL_GDTR + 2)

  /* Enable A20 line */
  xor     %ax, %ax
  in         $0x92, %al
  or         $2, %al
  out     %al, $0x92

  cli

  /* Load the GDT base address and limit from memory into the GDTR register */
  lgdt     LABEL_GDTR

   /* Enable protect mode */
  movl     %cr0, %eax
  orl     $1, %eax
  movl     %eax, %cr0

  /* Jump to protected-mode OS code */
  ljmp     $SegSelectorCode32, $0


LABEL_PE_LDT_CODE32:
.code32
  mov     $(SegSelectorData), %ax
  mov     %ax, %ds
  mov     $(SegSelectorVideo), %ax
  mov     %ax, %gs

  xorl     %esi, %esi
  xorl    %edi, %edi
  movl     $Msg2Offset, %esi
  movl     $((80 * 11 + 0) * 2), %edi
  movb     $0xC, %ah

ldt_dump_str:
  lodsb
  andb     %al, %al
  jz      ldt_fin
  mov     %ax, %gs:(%edi)
  addl     $2, %edi
  jmp     ldt_dump_str

ldt_fin:
  jmp .

.set LDT_CODE32_LEN, (. - LABEL_PE_LDT_CODE32)

# protected-mode OS code in GDT
LABEL_PE_CODE32:
.code32
  /* Load data segment selector */
  mov     $(SegSelectorData), %ax
  mov     %ax, %ds

  /* Load Video segment selector */
  mov     $(SegSelectorVideo), %ax
  mov     %ax, %gs

  /* Output the data */
  xorl     %esi, %esi
  xorl    %edi, %edi
  movl     $Msg1Offset, %esi
  movl     $((80 * 10 + 0) * 2), %edi
  movb     $0xC, %ah

dump_str:
  lodsb
  andb     %al, %al
  jz      fin
  mov     %ax, %gs:(%edi)
  addl     $2, %edi
  jmp     dump_str

fin:
  /* Load LDT selector */
  mov     $(SegSelectorLDT), %ax

  /* Load LDT selector in GDT to LDT register */
  lldt     %ax

  /* Jump to code segment in LDT */
  ljmp     $(SegSelectorLDTCode32), $0

.set PECode32Len, (. - LABEL_PE_CODE32)

os_msg:
  .ascii "Welcome to OS context!"
  .byte     0

  .org    0x200, 0x41 # fill characters with 'A'. Sector 2
Figure 2. Code for Operating System
16位元real mode程式碼 (os_main)中,執行若干任務如下所述:
- 設定LABEL_GDT_CODE的基底位址為PE_CODE32的起始位址
- 設定LABEL_GDT_DATA的基底位址為LABEL_DATA的起始位址
- 設定LABEL_GDT_LDT的基底位址為LABEL_LDT的起始位址
- 設定LABEL_LDT_ENTRY的基底位址為LABEL_PE_LDT_CODE32的起始位址
- 設定GDTPtr的基底位址為GDT的起始位址(也就是GDT_DESC_NULL)
- 開啟A20線路 (A20 Line)
- 將GDT的起始位址載入至GDTR暫存器
- 設定cr0暫存器的bit 0以便進入保護模式
- 使用ljmp指令跳至PE_CODE32程式碼
- 使用lldt指令將LDT的segment selector載入至LDTR (Local Descriptor Table Register),並跳至SegSelectorLDTCode32 segment selector執行LDT的程式碼。
pm.h標頭檔
/* pm.h
*
* Adrian Huang (adrianhuang0701@gmail.com)
*/
.macro SEG_DESC Base, Limit, Attr
   .2byte (\Limit & 0xFFFF)
  .2byte (\Base & 0xFFFF)
  .byte  ((\Base >> 16) & 0xFF)
  .2byte ((\Attr & 0xF0FF) | ((\Limit >> 8) & 0x0F00))
  .byte  ((\Base >> 24) & 0xFF)
.endm

.macro InitSegDescriptor OFFSET GDT_SEG_ADDR
  xor     %ax, %ax
  mov     %cs, %ax
  shl     $4, %eax
  addl    $(\OFFSET), %eax
  movw     %ax, (\GDT_SEG_ADDR + 2)
  shr     $16, %eax
  movb     %al, (\GDT_SEG_ADDR + 4)
  movb     %ah, (\GDT_SEG_ADDR + 7)

.endm

.set DESC_ATTR_TYPE_LDT,         0x82       /* LDT Segment         */
.set DESC_ATTR_TYPE_CD_ER,         0x9A     /* Code segment with Execute/Read */
.set DESC_ATTR_TYPE_CD_E,         0x98     /* Code segment with Execute Only */
.set DESC_ATTR_TYPE_CD_RW,         0x92    /* Data segment with R/W         */
.set DESC_ATTR_D,                 0x4000     /* 32-bit segment                 */

/* Selector Attribute */
.set SA_TIL,     0x4
.set SA_RPL0,     0x0
.set SA_RPL1,     0x1
.set SA_RPL2,     0x2
.set SA_RPL3,     0x3
編譯程式碼
請參照此篇的Makefile程式碼
其編譯訊息如下所示:
adrian@adrian-desktop:~/working/build_os/my_ex/04day/blog/pe-multi-seg-ldt$ make clean all
rm -f boot_loader.o os.o boot_loader.bin
gcc -c boot_loader.S
gcc -c os.S
ld -Ttext=0x7C00 -s boot_loader.o -o boot_loader.bin --oformat binary
ld -Ttext=0x0 -s os.o -o os.bin --oformat binary
ld: warning: cannot find entry symbol _start; defaulting to 0000000000000000
cat os.bin >> boot_loader.bin
adrian@adrian-desktop:~/working/build_os/my_ex/04day/blog/pe-multi-seg-ldt$
QEMU測試結果
【Reference】
[1] Solrex - 使用開源軟體-自己動手寫作業系統
[2] Intel 64 and IA-32 Architectures. Software Developer's Manual. Volume 3A
[3] 30天打造OS!作業系統自作入門
[4] Jserv's Blog
[5] X86 開機流程小記
[6] Linux assemblers: A comparison of GAS and NASM
[7] linux-source-2.6.31
2010年9月29日 星期三
[打造簡易作業系統 - 以GNU Assembler組合語言撰寫] (四) 由16位元真實模式 (Real Mode) 進入32位元保護模式 (Protect Mode)
前三篇文章所展示的程式碼都是CPU執行於真實模式 (Real Mode)。然而,一般作業系統運行於保護模式 (Protect Mode),其記憶體定址最高可至4GB (32位元)。故本文先介紹real mode與protect mode記憶體定址的方式。
Real mode與Protect mode記憶體定址介紹
Figure 1展示real mode記憶體定址方式,其觀念在於將邏輯位址(Logical Address)的區段(Segment)位址向左位移4個位元,再將其所得的位址加上位移值,如此便能轉換成線性位址 (Linear Address)。至於,邏輯位址該如何表示呢? 其表示法為"Address of Segment:Offset"
,例如: CS:IP、SS:SP、DS:SI和ES:DI,詳情請參考x86 Assembly Language。Figure 1描述一個簡單邏輯位址轉換線性位址的例子,因此不再贅述。

Figure 2展示保護模式記憶體定址方式,其觀念在於將區段 (Segment)看成區段選擇器 (Segment Selector),用此選擇器索引出對應的Segment Descriptor,如此便能索引32位元的基底位址 (32-bit base address),然後再加上位移植,便能轉換成線性位址。

保護模式相關課題之介紹
此段落將著重介紹保護模式相關課題之介紹,包含介紹GDT/LDT (GDTR/LDTR)、Segment Descriptor、Segment Selector、 和Memory Management Register
Global and Local Descriptor Table (GDT and LDT)
當CPU運行於保護模式時,所有的記憶體存取都必須經由GDT或LDT,此表格 (GDT or LDT)存放最小單元便是Segment Descriptor。每一個Segment Descriptor都有對應的segment selector,用以索引出對應的Segment Descriptor。
GDTR and LDTR (GDT Register and LDT Register)
GDTR與LDTR用以儲存GDT與LDT的起始位置,此設定必須在進入保護模式完成設定。Figure 3展示GDTR與LDTR格式,其中GDTR包含32位元的基底位址與16位元的長度限制。而LDTR多增加了16位元的segment selector。

Segment Descriptor
Segment Descriptor為Descriptor Table組成的基本元素,其長度為8位元組。如Figure 4所示,可分為三大類: 1. 32位元的基底位址 (Base Address), 2. 20位元的區段限制 (Segment Limit), 3. 區段屬性。細節請參考Intel 64 and IA-32 Architectures. Software Developer's Manual. Volume 3A
Segment Selector
Figure 5展示Segment Selector示意圖,其目的用來索引對應的Segment Descriptor。因Descriptor Index有13個位元,故Descriptor個數最大可至8192。

Boot Loader程式碼
作業系統程式碼
此作業系統程式碼運行於32位元保護模式,一開始定義三個Segment Descriptor (NULL, CODE32與VIDEO),其中VIDEO的基底位址為0xB8000,詳情請參考Printing to Screen。接著定義GDT的長度、定義Code32與VIDEO的segment selector、定義GDTPtr。
16位元real mode程式碼 (os_main)中,執行若干任務如下所述:
pm.h標頭檔
編譯程式碼
下圖為編譯的Makefile。
其編譯訊息如下所示:
QEMU測試結果

【Reference】
[1] Solrex - 使用開源軟體-自己動手寫作業系統
[2] Intel 64 and IA-32 Architectures. Software Developer's Manual. Volume 3A
[3] 30天打造OS!作業系統自作入門
[4] Jserv's Blog
[5] X86 開機流程小記
[6] Linux assemblers: A comparison of GAS and NASM
[7] linux-source-2.6.31
Real mode與Protect mode記憶體定址介紹
Figure 1展示real mode記憶體定址方式,其觀念在於將邏輯位址(Logical Address)的區段(Segment)位址向左位移4個位元,再將其所得的位址加上位移值,如此便能轉換成線性位址 (Linear Address)。至於,邏輯位址該如何表示呢? 其表示法為"Address of Segment:Offset"
,例如: CS:IP、SS:SP、DS:SI和ES:DI,詳情請參考x86 Assembly Language。Figure 1描述一個簡單邏輯位址轉換線性位址的例子,因此不再贅述。
Figure 1. Memory Segmentation in Real Mode
Figure 2展示保護模式記憶體定址方式,其觀念在於將區段 (Segment)看成區段選擇器 (Segment Selector),用此選擇器索引出對應的Segment Descriptor,如此便能索引32位元的基底位址 (32-bit base address),然後再加上位移植,便能轉換成線性位址。
Figure 2. Memory Segment in Protect Mode
保護模式相關課題之介紹
此段落將著重介紹保護模式相關課題之介紹,包含介紹GDT/LDT (GDTR/LDTR)、Segment Descriptor、Segment Selector、 和Memory Management Register
Global and Local Descriptor Table (GDT and LDT)
當CPU運行於保護模式時,所有的記憶體存取都必須經由GDT或LDT,此表格 (GDT or LDT)存放最小單元便是Segment Descriptor。每一個Segment Descriptor都有對應的segment selector,用以索引出對應的Segment Descriptor。
GDTR and LDTR (GDT Register and LDT Register)
GDTR與LDTR用以儲存GDT與LDT的起始位置,此設定必須在進入保護模式完成設定。Figure 3展示GDTR與LDTR格式,其中GDTR包含32位元的基底位址與16位元的長度限制。而LDTR多增加了16位元的segment selector。
Figure 3. Memory Management Register
Segment Descriptor
Segment Descriptor為Descriptor Table組成的基本元素,其長度為8位元組。如Figure 4所示,可分為三大類: 1. 32位元的基底位址 (Base Address), 2. 20位元的區段限制 (Segment Limit), 3. 區段屬性。細節請參考Intel 64 and IA-32 Architectures. Software Developer's Manual. Volume 3A
Figure 4. Segment Descriptor [2]
Segment Selector
Figure 5展示Segment Selector示意圖,其目的用來索引對應的Segment Descriptor。因Descriptor Index有13個位元,故Descriptor個數最大可至8192。
Figure 5. Segment Selector
Boot Loader程式碼
/* boot_loader.S
*
* Copyright (C) 2010 Adrian Huang (adrianhuang0701@gmail.com)
*
* This code is intended to simulate a simplified boot loader. This boot
* loader loads 3 sectors into the physical memory and jumps the entry
* point of OS.
*
*/
.code16.text.set BOOT_SEG, 0x07C0 /* starting code segment (CS) of boot loader */
.set OS_SEG, 0x0900 /* code segment address of OS entry point */
.set OS_OFFSET, 0x0000 /* the offset address of OS entry point */
.global _start
_start:
# FAT12 file system format
jmp start_prog # jmp instruction
.byte 0x90
.ascii "ADRIAN " # OEM name (8 bytes)
.word 512 # Bytes per sector
.byte 1 # Sector per cluster
.word 1 # Reserved sector count: should be 1 for FAT12
.byte 2 # Number of file allocation tables.
.word 224 # Maximum number of root directory entries.
.word 2880 # Total sectors
.byte 0xf0 # Media descriptor:
.word 9 # Sectors per File Allocation Table
.word 18 # Sectors per track
.word 2 # Number of heads
.long 0 # Count of hidden sectors
.long 0 # Total sectors
.byte 0 # Physical driver number
.byte 0 # Reserved
.byte 0x29 # Extended boot signature
.long 0x12345678 # Serial Number
.ascii "HELLO-OS " # Volume Label
.ascii "FAT12 " # FAT file system type
.fill 18, 1, 0 # fill 18 characters with zero
start_prog:
# initialize the register with cs register
movw %cs, %ax
movw %ax, %ds
movw %ax, %es
movw %ax, %ss
xorw %sp, %sp
cld # clear direction flag
sti # set interrupt flag
# The following code is loaded three sectors (2-4th sectors from boot.bin)
# into the physical memory 0x8000-0x85FF.
movw $OS_SEG, %ax
mov %ax, %es # ES:BX-> destination buffer address pointer
movw $OS_OFFSET, %bx
movb $2, %cl # sector
cont:
movb $0x02, %ah # Read sectors from drive
movb $0x1, %al # Sectors to read count
movb $0x0, %ch # track
movb $0x0, %dh # head
movb $0, %dl # drive
int $0x13 # trigger a interrupt 0x13 service
jc fail # the clear flag is set if the operation is failed
mov %es, %ax
addw $0x20, %ax # move to the next sector
movw %ax, %es # move to the next sector
incb %cl
cmpb $3, %cl # has finished reading 3 sectors?
jbe cont # continue to read the sector
jmp os_entry # jump to OS entry point
fail:
movw $err_msg, %si
fail_loop:
lodsb
andb %al, %al
jz end
movb $0x0e, %ah
int $0x10
jmp fail_loop
os_entry:
ljmp $OS_SEG, $OS_OFFSET # jump to os context
end:
hlt
jmp end
err_msg:
.ascii "Reading sectors operation is failed!"
.byte 0
.org 0x1FE, 0x41 # fill the rest of characters with zero until the 254th character
# Boot sector signature
.byte 0x55
.byte 0xaa
作業系統程式碼
此作業系統程式碼運行於32位元保護模式,一開始定義三個Segment Descriptor (NULL, CODE32與VIDEO),其中VIDEO的基底位址為0xB8000,詳情請參考Printing to Screen。接著定義GDT的長度、定義Code32與VIDEO的segment selector、定義GDTPtr。
16位元real mode程式碼 (os_main)中,執行若干任務如下所述:
- 設定Code32的基底位址為PE_CODE32的起始位址
- 設定GDTPtr的基底位址為GDT的起始位址(也就是GDT_DESC_NULL)
- 開啟A20線路 (A20 Line)
- 將GDT的起始位址載入至GDTR暫存器
- 設定cr0暫存器的bit 0以便進入保護模式
- 使用ljmp指令跳至PE_CODE32程式碼
/* os.S
*
* Adrian Huang (adrianhuang0701@gmail.com)
*
* This code is OS context for protected-mode.
*
*/
#include "pm.h"

.code16
.text
jmp os_main

# Segment descritors for GDT
GDT_DESC_NULL: SEG_DESC      0, 0, 0
GDT_DESC_CODE32: SEG_DESC    0, (PECode32Len - 1), (DESC_ATTR_TYPE_CD_ER | DESC_ATTR_D)
GDT_DESC_VIDEO: SEG_DESC     0xB8000, 0xFFFF, (DESC_ATTR_TYPE_CD_RW)

# The length of GDT
.set GdtLen, (. - GDT_DESC_NULL)

# Segment selectors for code segment and video output
.set SegSelectorCode32, (GDT_DESC_CODE32 - GDT_DESC_NULL)
.set SegSelectorVideo,  (GDT_DESC_VIDEO - GDT_DESC_NULL)

# GDTR pointer
GDTPtr:
.2byte (GdtLen - 1)     # Limit field
.4byte 0                 # base field

# real-mode OS code
os_main:
mov %cs, %ax
mov %ax, %ds
mov %ax, %ss
mov %ax, %es


/* Set gdt for code segment */
InitSegDescriptor PE_CODE32, GDT_DESC_CODE32

/* Set GDTR */
xor     %ax, %ax
mov     %cs, %ax
shl     $4, %eax
addl    $GDT_DESC_NULL, %eax
movl     %eax, (GDTPtr + 2)

/* Enable A20 line */
xor     %ax,   %ax
in      $0x92, %al
or      $2,    %al
out     %al,   $0x92

cli

/* Load the GDT base address and limit from memory into the GDTR register */
lgdt     GDTPtr

/* Enable protect mode */
movl     %cr0, %eax
orl      $1,   %eax
movl     %eax, %cr0

/* Jump to protected-mode OS code */
ljmp     $SegSelectorCode32, $0


# protected-mode OS code
PE_CODE32:
.code32
/* Load Video segment selector */
mov     $(SegSelectorVideo), %ax
mov     %ax, %gs

/* Output the data */
movl    $((80 * 10 + 0) * 2), %edi
movb    $0xC, %ah
movb    $'H', %al
mov     %ax, %gs:(%edi)

jmp .

.set PECode32Len, (. - PE_CODE32)

os_msg:
.ascii "Welcome to OS context!"
.byte     0

.org    0x200, 0x41 # fill characters with 'A'. Sector 2
pm.h標頭檔
/* pm.h
*
* Adrian Huang (adrianhuang0701@gmail.com)
*/


.macro SEG_DESC Base, Limit, Attr
.2byte (\Limit & 0xFFFF)
.2byte (\Base & 0xFFFF)
.byte  ((\Base >> 16) & 0xFF)
.2byte ((\Attr & 0xF0FF) | ((\Limit >> 8) & 0x0F00))
.byte  ((\Base >> 24) & 0xFF)
.endm

.macro InitSegDescriptor OFFSET GDT_SEG_ADDR
xor     %ax, %ax
mov     %cs, %ax
shl     $4, %eax
addl    $(\OFFSET), %eax
movw    %ax, (\GDT_SEG_ADDR + 2)
shr     $16, %eax
movb    %al, (\GDT_SEG_ADDR + 4)
movb    %ah, (\GDT_SEG_ADDR + 7)

.endm

.set DESC_ATTR_TYPE_LDT,         0x82     /* LDT Segment                    */
.set DESC_ATTR_TYPE_CD_ER,       0x9A     /* Code segment with Execute/Read */
.set DESC_ATTR_TYPE_CD_E,        0x98     /* Code segment with Execute Only */
.set DESC_ATTR_TYPE_CD_RW,       0x92     /* Data segment with R/W          */
.set DESC_ATTR_D,                0x4000   /* 32-bit segment                 */

/* Selector Attribute */
.set SA_TIL,      0x4
.set SA_RPL0,     0x0
.set SA_RPL1,     0x1
.set SA_RPL2,     0x2
.set SA_RPL3,     0x3
編譯程式碼
下圖為編譯的Makefile。
LD=ld
CC=gcc

all: boot_loader.bin

boot_loader.bin: boot_loader.o os.o
${LD} -Ttext=0x7C00 -s $< -o $@ --oformat binary
${LD} -Ttext=0x0 -s os.o -o os.bin --oformat binary
cat os.bin >> $@

boot_loader.o:
${CC} -c boot_loader.S

os.o:
${CC} -c os.S

clean:
rm -f boot_loader.o os.o os.bin boot_loader.bin
其編譯訊息如下所示:
adrian@adrian-desktop:~/working/build_os/my_ex/04day/pe-orig-makefile$ make all
gcc -c boot_loader.S
gcc -c os.S
ld -Ttext=0x7C00 -s boot_loader.o -o boot_loader.bin --oformat binary
ld -Ttext=0x0 -s os.o -o os.bin --oformat binary
ld: warning: cannot find entry symbol _start; defaulting to 0000000000000000
cat os.bin >> boot_loader.bin
QEMU測試結果
【Reference】
[1] Solrex - 使用開源軟體-自己動手寫作業系統
[2] Intel 64 and IA-32 Architectures. Software Developer's Manual. Volume 3A
[3] 30天打造OS!作業系統自作入門
[4] Jserv's Blog
[5] X86 開機流程小記
[6] Linux assemblers: A comparison of GAS and NASM
[7] linux-source-2.6.31
2010年8月31日 星期二
[打造簡易作業系統 - 以GNU Assembler組合語言撰寫] (三) Boot Loader + 作業系統載入實例 (CF Card)
上篇說明如何撰寫小型Boot Loader將作業系統載入至記憶體並執行該作業系統程式碼,並利用qemu實現。為了更真實性,本篇將boot loader及作業系統安裝在CF card並利用CF card開機,用以證明該boot loader及作業系統可以正確地在實體機器上運行。
將DL暫存器更改為0x80
由於上篇是使用軟碟機開機,因此在使用BIOS中斷服務0x13時 (AH=02 Read Sectors from Driver),需將DL暫存器設定為0(0代表軟碟機0,1代表軟碟機1),但因為現在要從硬碟讀取,所以需將DL設定為0x80,即底下範例程式紅色部份。
Boot Loader範例程式 (以FAT32為範例)
作業系統程式碼與編譯
請參照這篇的"作業系統程式碼"與"編譯程式碼"。
安裝boot_loader.bin安裝至CF card
測試結果
將該系統重開並選擇CF Card開機,其畫面如下:

【Reference】
1.30天打造OS!作業系統自作入門
2. Jserv's Blog
3. X86 開機流程小記
4. Linux assemblers: A comparison of GAS and NASM
5. linux-source-2.6.31
將DL暫存器更改為0x80
由於上篇是使用軟碟機開機,因此在使用BIOS中斷服務0x13時 (AH=02 Read Sectors from Driver),需將DL暫存器設定為0(0代表軟碟機0,1代表軟碟機1),但因為現在要從硬碟讀取,所以需將DL設定為0x80,即底下範例程式紅色部份。
Boot Loader範例程式 (以FAT32為範例)
/* boot_loader.S
*
* Copyright (C) 2010 Adrian Huang (adrianhuang0701@gmail.com)
*
* This code is intended to simulate a simplified boot loader. This boot
* loader loads 3 sectors into the physical memory and jumps the entry
* point of OS.
*
*/

BOOT_SEG     = 0x07C0    /* starting code segment (CS) of boot loader */
OS_SEG       = 0x0800    /* code segment address of OS entry point */
OS_OFFSET    = 0x0000    /* the offset address of OS entry point */

 .code16

 .section .text

 .global _start
_start:
 # FAT12 file system format
 ljmp     $BOOT_SEG, $start_prog         # jmp instruction

 .byte     0x90
 .ascii    "ADRIAN  "        # OEM name (8 bytes)
 .word     512               # Bytes per sector
 .byte     1                 # Sector per cluster
 .word     32                # Reserved sector count: should be 32 for FAT32
 .byte     2                 # Number of file allocation tables.
 .word     0                 # Maximum number of root directory entries. 0 for FAT32
 .word     0                 # Total sectors
 .byte     0xf8              # Media descriptor: fix disk
 .word     9                 # Sectors per File Allocation Table
 .word     18                # Sectors per track
 .word     2                 # Number of heads
 .long     0                 # Count of hidden sectors
 .long     2030112           # Total sectors
 .byte     0                 # Physical driver number
 .byte     0                 # Reserved
 .byte     0x29              # Extended boot signature
 .long     0x12345678        # Serial Number
 .ascii    "HELLO-OS   "     # Volume Label
 .ascii    "FAT12   "        # FAT file system type
 .fill     18, 1, 0          # fill 18 characters with zero

start_prog:
 # initialize the register with cs register
 movw    %cs, %ax
 movw    %ax, %ds
 movw    %ax, %es
 movw    %ax, %ss
 xorw    %sp, %sp

 cld                     # clear direction flag
 sti                     # set interrupt flag

 # The following code is loaded three sectors (2-4th sectors from boot.bin)
 # into the physical memory 0x8000-0x85FF.
 movw    $OS_SEG,     %ax
 mov     %ax,         %es  # ES:BX-> destination buffer address pointer
 movb    $2,          %cl  # sector


cont:
 movw     $0,    %bx
 movb     $0x02, %ah  # Read sectors from drive
 movb     $0x1,  %al  # Sectors to read count
 movb     $0x0,  %ch  # track
 movb     $0x0,  %dh  # head
 movb     $0x80, %dl  # drive

 int      $0x13        # trigger a interrupt 0x13 service
 jc       fail         # the clear flag is set if the operation is failed

 mov      %es, %ax
 addw     $0x20, %ax     # move to the next sector
 movw     %ax, %es       # move to the next sector
 incb     %cl
 cmpb     $3, %cl        # has finished reading 3 sectors?
 jbe      cont           # continue to read the sector

 jmp  os_entry           # jump to OS entry point

fail:
 movw     $err_msg, %si
fail_loop:
 lodsb
 andb     %al, %al
 jz       end
 movb     $0x0e, %ah
 int      $0x10
 jmp      fail_loop


os_entry:
 ljmp $OS_SEG, $OS_OFFSET  # jump to os context

end:
 hlt

err_msg:
 .ascii "Reading sectors operation is failed!"
 .byte     0

 .org 0x1FE, 0x41 # fill the rest of characters with zero until the 254th character

 # Boot sector signature
 .byte     0x55
 .byte     0xaa
作業系統程式碼與編譯
請參照這篇的"作業系統程式碼"與"編譯程式碼"。
安裝boot_loader.bin安裝至CF card
adrian@adrian-mem1:~/img$ sudo dd if=./boot_loader.bin of=/dev/sda
測試結果
將該系統重開並選擇CF Card開機,其畫面如下:
【Reference】
1.30天打造OS!作業系統自作入門
2. Jserv's Blog
3. X86 開機流程小記
4. Linux assemblers: A comparison of GAS and NASM
5. linux-source-2.6.31
2010年8月20日 星期五
Google將推出Chrome作業系統的平板電腦
Google將與HTC合作,以Google Chrome作業系統開發平板電腦,預計今年11月26發表。
詳見: First Chrome OS Tablet Set for Black Friday Debut
文中還提及為什麼不使用Android的原因。
詳見: First Chrome OS Tablet Set for Black Friday Debut
文中還提及為什麼不使用Android的原因。
2010年8月13日 星期五
Google大神開始對Linux Kernel Source貢獻了
Linux 2.6.35有Google大神的程式碼了!! (跪拜0rz......)
其主要提升網路封包處理速度
詳見: Linux 2.6.35 Includes Speedy Google Code, Less Bloat
其主要提升網路封包處理速度
詳見: Linux 2.6.35 Includes Speedy Google Code, Less Bloat
2010年8月11日 星期三
[打造簡易作業系統 - 以GNU Assembler組合語言撰寫] (二) Boot Loader + 作業系統載入實例 (QEMU)
繼上篇說明如何撰寫開機Hello World,本篇文章說明如何撰寫簡單的Boot Loader跟一個只會印出訊息的作業系統。
小型Boot Loader設計概念
筆者所撰寫的小型Boot Loader於BIOS開機成功後,會被載入至實體記憶體位址0x7C00並跳至此位址執行boot loader的程式碼,此boot loader程式碼會將作業系統程式碼 (僅三個磁區),載入實體記憶體位址0x8000並跳至此位址執行作業系統的程式碼,然而此作業系統別無功能,僅會印出簡單的訊息。如此便能模擬一般boot loader載入作業系統的程序。
圖二為boot loader將作業系統載入實體記憶體位址示意圖,至於為什麼會選擇0x8000開始存放作業系統程式碼,其原因是x86系統規範位址0x7E00-0x7FFFF為conventional memory,因此筆者就挑0x8000來存放程式碼。
圖二、Boot Loader + OS Physical Memory Layout
Boot Loader程式碼下圖為Boot Loader程式碼,其運作原理在此稍作描述。首先,boot_loader透過.byte、.word、.long跟.ascii等指令將此磁區描述為一個FAT12檔案系統。接著,利用中斷服務編號0x13將作業系統的三個磁區讀入0x8000實體記憶體位址。如果讀取失敗的話,則利用中斷服務編號0x010印出錯誤訊息。特別要提出的是,程式碼使用兩次遠程跳躍 (Far Dump),其原型ljmp code_segment_address, relative_address,例如: ljmp $BOOT_SEG, $start_prog代表code segment設定為0x07C0加上start_prog標籤的位址,即0x7C00+start_prog位址,此為Intel x86 CPU memory segmentation機制。透過此設定,boot loader程式碼便能正確地在0x7C00位址執行。另一個ljmp,ljmp $OS_SEG, $OS_OFFSET,因為boot loader將作業系統程式碼放在0x8000實體記憶體位址,因此code segment必須設為0x0800,以便讓作業系統程式碼可以正確地執行。
下圖為編譯的Makefile。
小型Boot Loader設計概念
筆者所撰寫的小型Boot Loader於BIOS開機成功後,會被載入至實體記憶體位址0x7C00並跳至此位址執行boot loader的程式碼,此boot loader程式碼會將作業系統程式碼 (僅三個磁區),載入實體記憶體位址0x8000並跳至此位址執行作業系統的程式碼,然而此作業系統別無功能,僅會印出簡單的訊息。如此便能模擬一般boot loader載入作業系統的程序。
圖一為筆者所編譯出來的plain binary file,此程式碼僅有四個磁區 (共2048 bytes),0x0-0x1ff為boot loader磁區,0x200-0x7ff為作業系統的三個磁區,雖然,真正的作業系統程式碼在0x200-0x3ff,其它兩個磁區僅填入字元'B'與'C',但筆者還是把這三個磁區稱為作業系統程式碼,因為boot loader會將這三個磁區載入實體記憶體位址0x8000。
圖一、Boot + OS Binary Image Layout |
圖二為boot loader將作業系統載入實體記憶體位址示意圖,至於為什麼會選擇0x8000開始存放作業系統程式碼,其原因是x86系統規範位址0x7E00-0x7FFFF為conventional memory,因此筆者就挑0x8000來存放程式碼。
 |
Boot Loader程式碼
/* boot_loader.S
*
* Copyright (C) 2010 Adrian Huang (adrianhuang0701@gmail.com)
*
* This code is intended to simulate a simplified boot loader. This boot
* loader loads 3 sectors into the physical memory and jumps the entry
* point of OS.
*
*/

BOOT_SEG     = 0x07C0       /* starting code segment (CS) of boot loader */
OS_SEG       = 0x0800       /* code segment address of OS entry point */
OS_OFFSET    = 0x0000       /* the offset address of OS entry point */

.code16

.section .text

.global _start
_start:
# FAT12 file system format
ljmp     $BOOT_SEG, $start_prog   # jmp instruction

.byte   0x90
.ascii  "ADRIAN  "                # OEM name (8 bytes)
.word   512                       # Bytes per sector
.byte   1                         # Sector per cluster
.word   1                         # Reserved sector count: should be 1 for FAT12
.byte   2                         # Number of file allocation tables.
.word   224                       # Maximum number of root directory entries.
.word   2880                      # Total sectors
.byte   0xf0                      # Media descriptor
.word   9                         # Sectors per File Allocation Table
.word   18                        # Sectors per track
.word   2                         # Number of heads
.long   0                         # Count of hidden sectors
.long   2880                      # Total sectors: 18 (sectors per track) * 2 (heads) * 80 (sectors) = 2880
.byte   0                         # Physical driver number
.byte   0                         # Reserved
.byte   0x29                      # Extended boot signature
.long   0x12345678                # Serial Number
.ascii  "HELLO-OS   "             # Volume Label
.ascii  "FAT12   "                # FAT file system type
.fill   18, 1, 0                  # fill 18 characters with zero

start_prog:
# initialize the register with cs register
movw    %cs, %ax
movw    %ax, %ds
movw    %ax, %es
movw    %ax, %ss
xorw    %sp, %sp

cld                     # clear direction flag
sti                     # set interrupt flag

# The following code is loaded three sectors (2-4th sectors from boot.bin)
# into the physical memory 0x8000-0x85FF.
movw    $OS_SEG,     %ax
mov     %ax,         %es  # ES:BX-> destination buffer address pointer
movb    $2,          %cl  # sector


cont:
movw     $0,    %bx
movb     $0x02, %ah     # Read sectors from drive
movb     $0x1,  %al     # Sectors to read count
movb     $0x0,  %ch     # track
movb     $0x0,  %dh     # head
movb     $0,    %dl     # drive

int      $0x13          # trigger a interrupt 0x13 service
jc       fail           # the clear flag is set if the operation is failed

mov     %es, %ax
addw    $0x20, %ax      # move to the next sector
movw    %ax, %es        # move to the next sector
incb    %cl
cmpb    $3, %cl         # has finished reading 3 sectors?
jbe     cont            # continue to read the sector

jmp  os_entry           # jump to OS entry point

fail:
movw    $err_msg, %si
fail_loop:
lodsb
andb    %al, %al
jz      end
movb    $0x0e, %ah
int     $0x10
jmp     fail_loop


os_entry:
ljmp $OS_SEG, $OS_OFFSET  # jump to os context

end:
hlt

err_msg:
.ascii "Reading sectors operation is failed!"
.byte     0

.org 0x1FE, 0x41 # fill the rest of characters with zero until the 254th character

# Boot sector signature
.byte     0x55
.byte     0xaa
作業系統程式碼
此段程式碼僅將訊息輸出至螢幕上,所以不再贅述。編譯程式碼/* os.S** Copyright (C) 2010 Adrian Huang (adrianhuang0701@gmail.com)** This code is OS context.**/.code16.section .text.global mainmain:movw %cs, %axmovw %ax, %dsmovw %ax, %esmovw %ax, %ssxorw %sp, %spcld # clear direction flagsti # set interrupt flagmovw $os_msg, %siload_msg:lodsbandb %al, %aljz os_finmovb $0x0e, %ahint $0x10jmp load_msgos_fin:hltjmp os_finos_msg:.ascii "Welcome to OS context!".byte 0.org 0x200, 0x41 # fill characters with 'A'. Sector 1.org 0x400, 0x42 # fill characters with 'B'. Sector 2.org 0x600, 0x43 # fill characters with 'C'. Sector 3
下圖為編譯的Makefile。
其編譯訊息如下所示:LD=ldCC=gccall: boot_loader.binboot_loader.bin: boot_loader.o os.o${LD} -Ttext=0x0 -s $< -o $@ --oformat binary${LD} -Ttext=0x0 -s os.o -o os.bin --oformat binarycat os.bin >> $@boot_loader.o:${CC} -c boot_loader.Sos.o:${CC} -c os.Sclean:rm -f boot_loader.o boot_loader.bin os.o
adrian@adrian-desktop:~/working/build_os/my_ex/boot_loader$ make clean allrm -f boot_loader.o boot_loader.bin os.ogcc -c boot_loader.Sgcc -c os.Sld -Ttext=0x0 -s boot_loader.o -o boot_loader.bin --oformat binaryld -Ttext=0x0 -s os.o -o os.bin --oformat binaryld: warning: cannot find entry symbol _start; defaulting to 0000000000000000cat os.bin >> boot_loader.binadrian@adrian-desktop:~/working/build_os/my_ex/boot_loader$
測試結果
 |
為了驗證作業系統的程式碼正確地載入實體記憶體位址0x8000,筆者利用xxd工具將boot_loader.bin dump出來,下圖為其結果。紅色框框為作業系統程式碼的十六進制碼。
 |
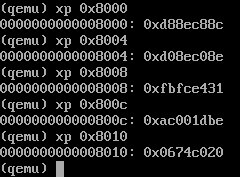
下圖中,筆者利用qemu提供的xp工具將0x8000-0x8010的內容dump出來,用以跟上圖0x200-0x210比對,比較上、下這兩張圖,可以證明作業系統程式碼正確地被載入至0x8000。
 |
【Reference】
2. Jserv's Blog
3. X86 開機流程小記
5. linux-source-2.6.31
訂閱:
文章 (Atom)